You Have ISO 27001. How Much SOC 2 Is Already Done?
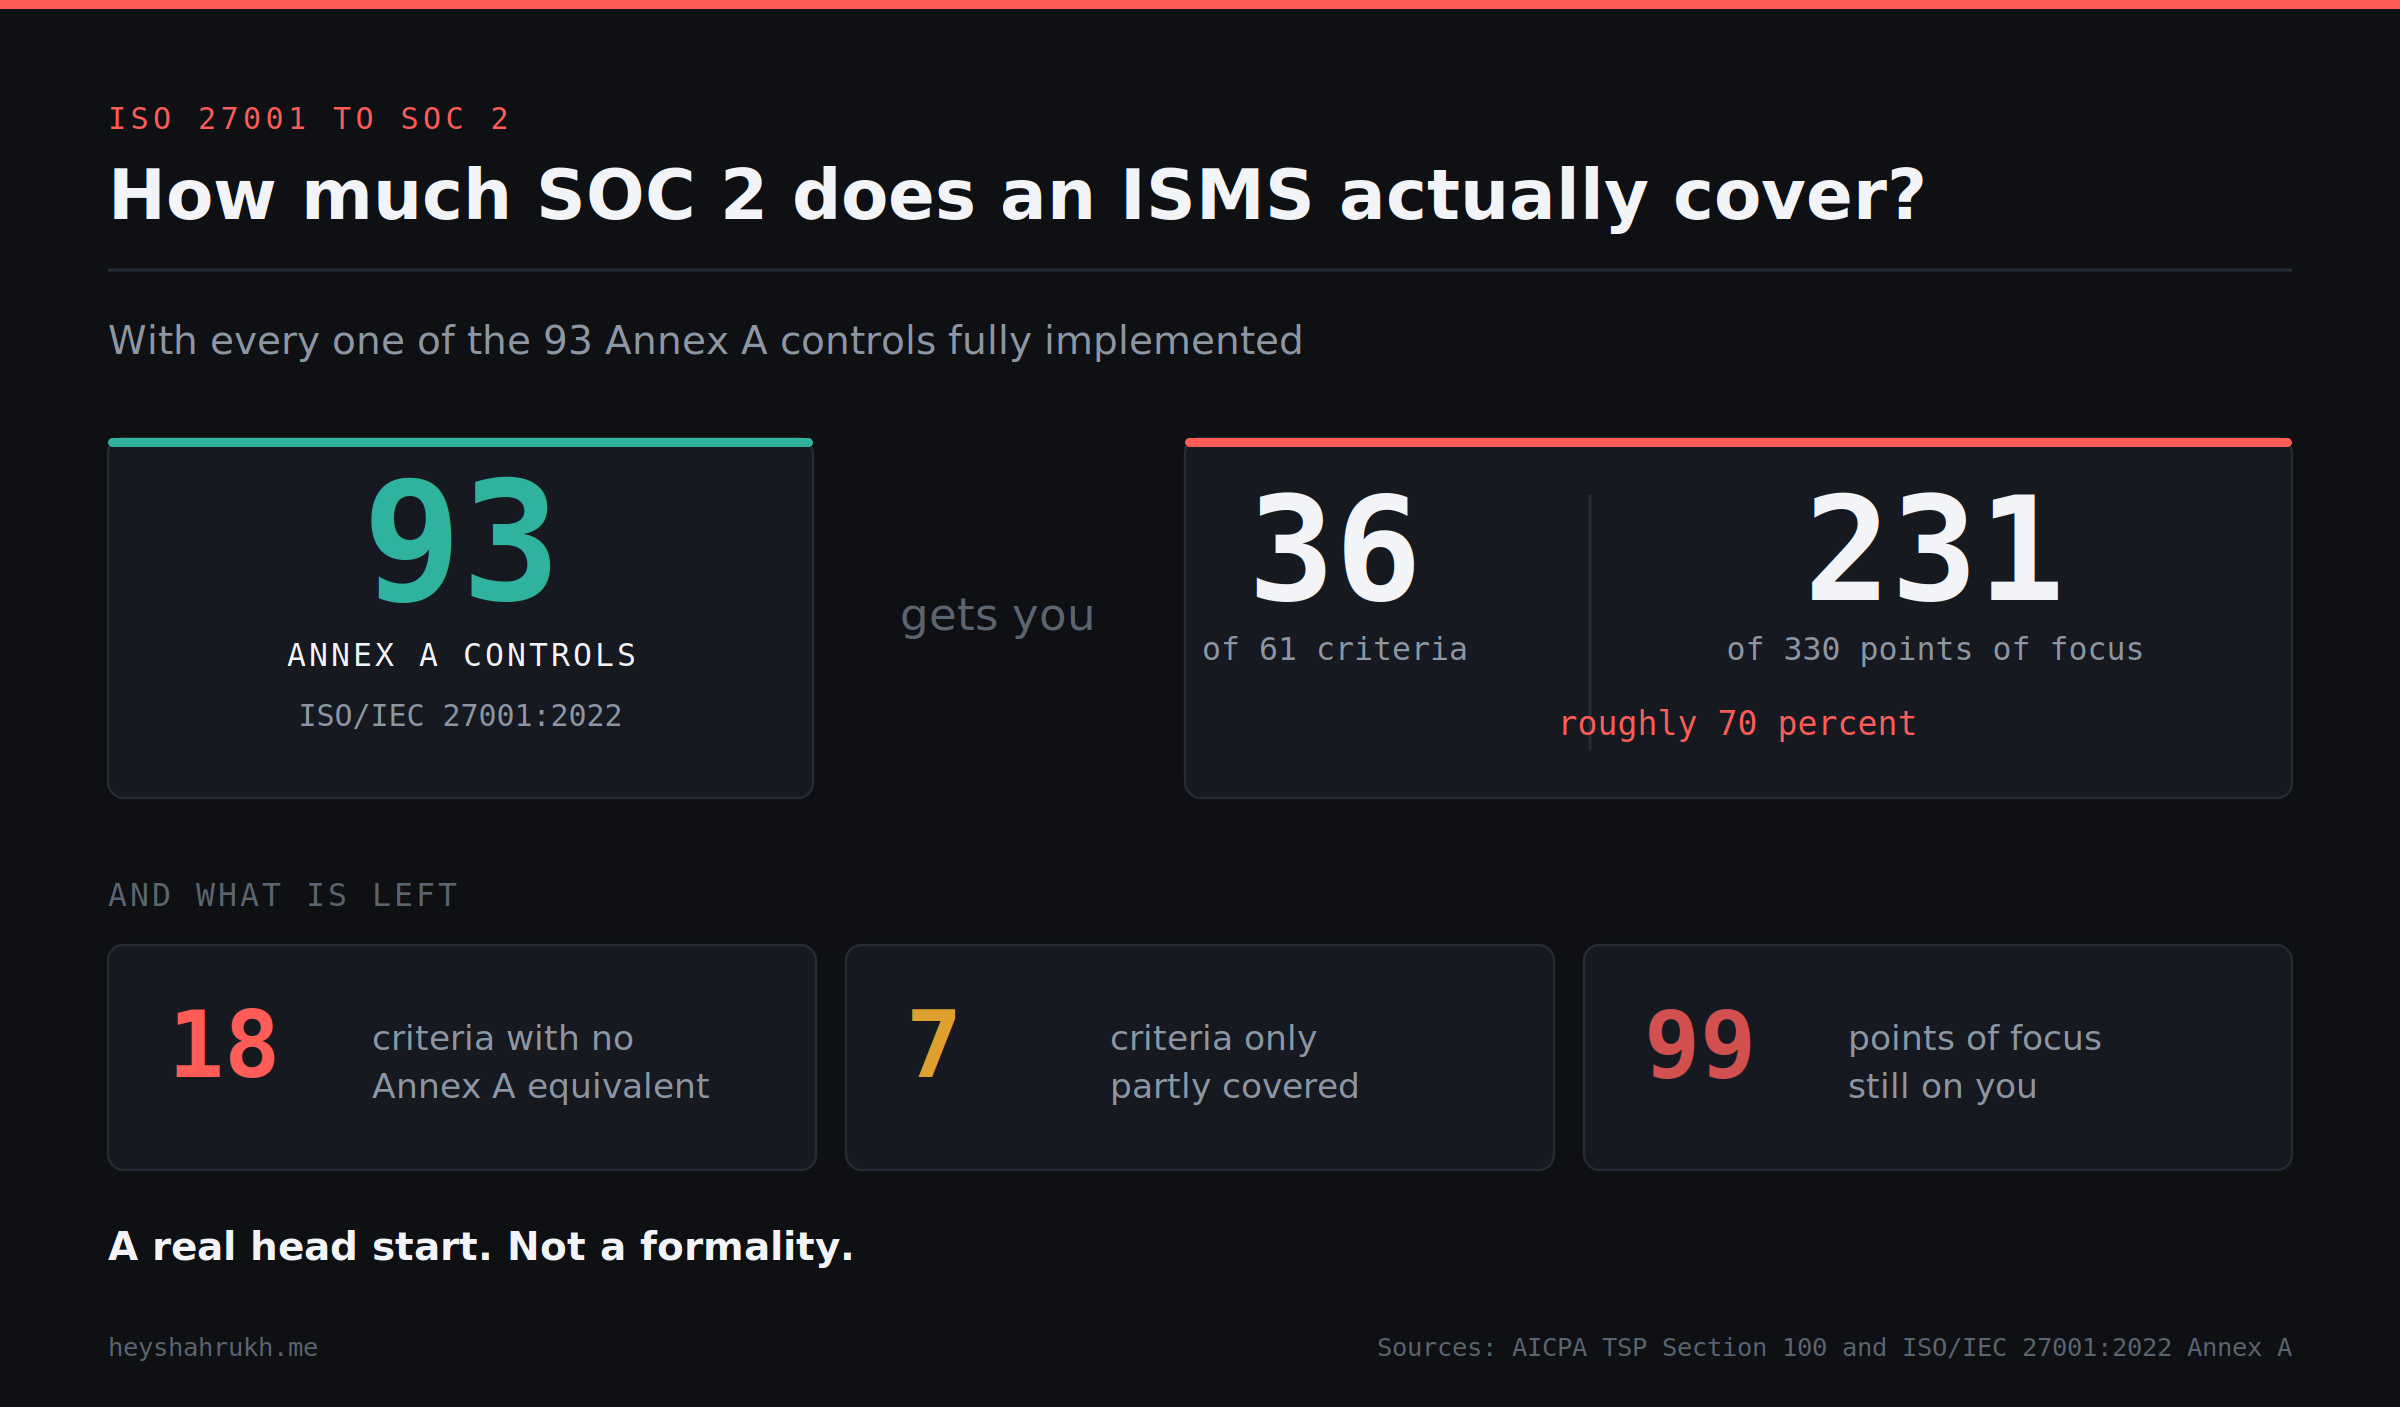
All 93 Annex A controls mapped to SOC 2. A complete ISMS covers 36 of 61 criteria and 231 of 330 points of focus. The gap is almost entirely privacy.
A US buyer asks for a SOC 2 report. The company already holds ISO 27001. Someone in the room says the sentence I have heard on almost every one of these calls: we already have an ISMS, so this should mostly be a formality.
Fair instinct. The problem is that "mostly" is carrying a great deal of weight, and nobody can size it until someone actually maps it. So I mapped all 93 Annex A controls from ISO/IEC 27001:2022 against all 61 SOC 2 criteria.
The short answer
With every Annex A control fully implemented:
36 of 61 SOC 2 criteria fully covered 7 partly covered 18 with no ISO equivalent at all 231 of 330 points of focus supported
Roughly seventy percent. That is a real head start and nobody should dismiss it. It also means the remaining thirty percent is not spread evenly across the standard.
Where it maps
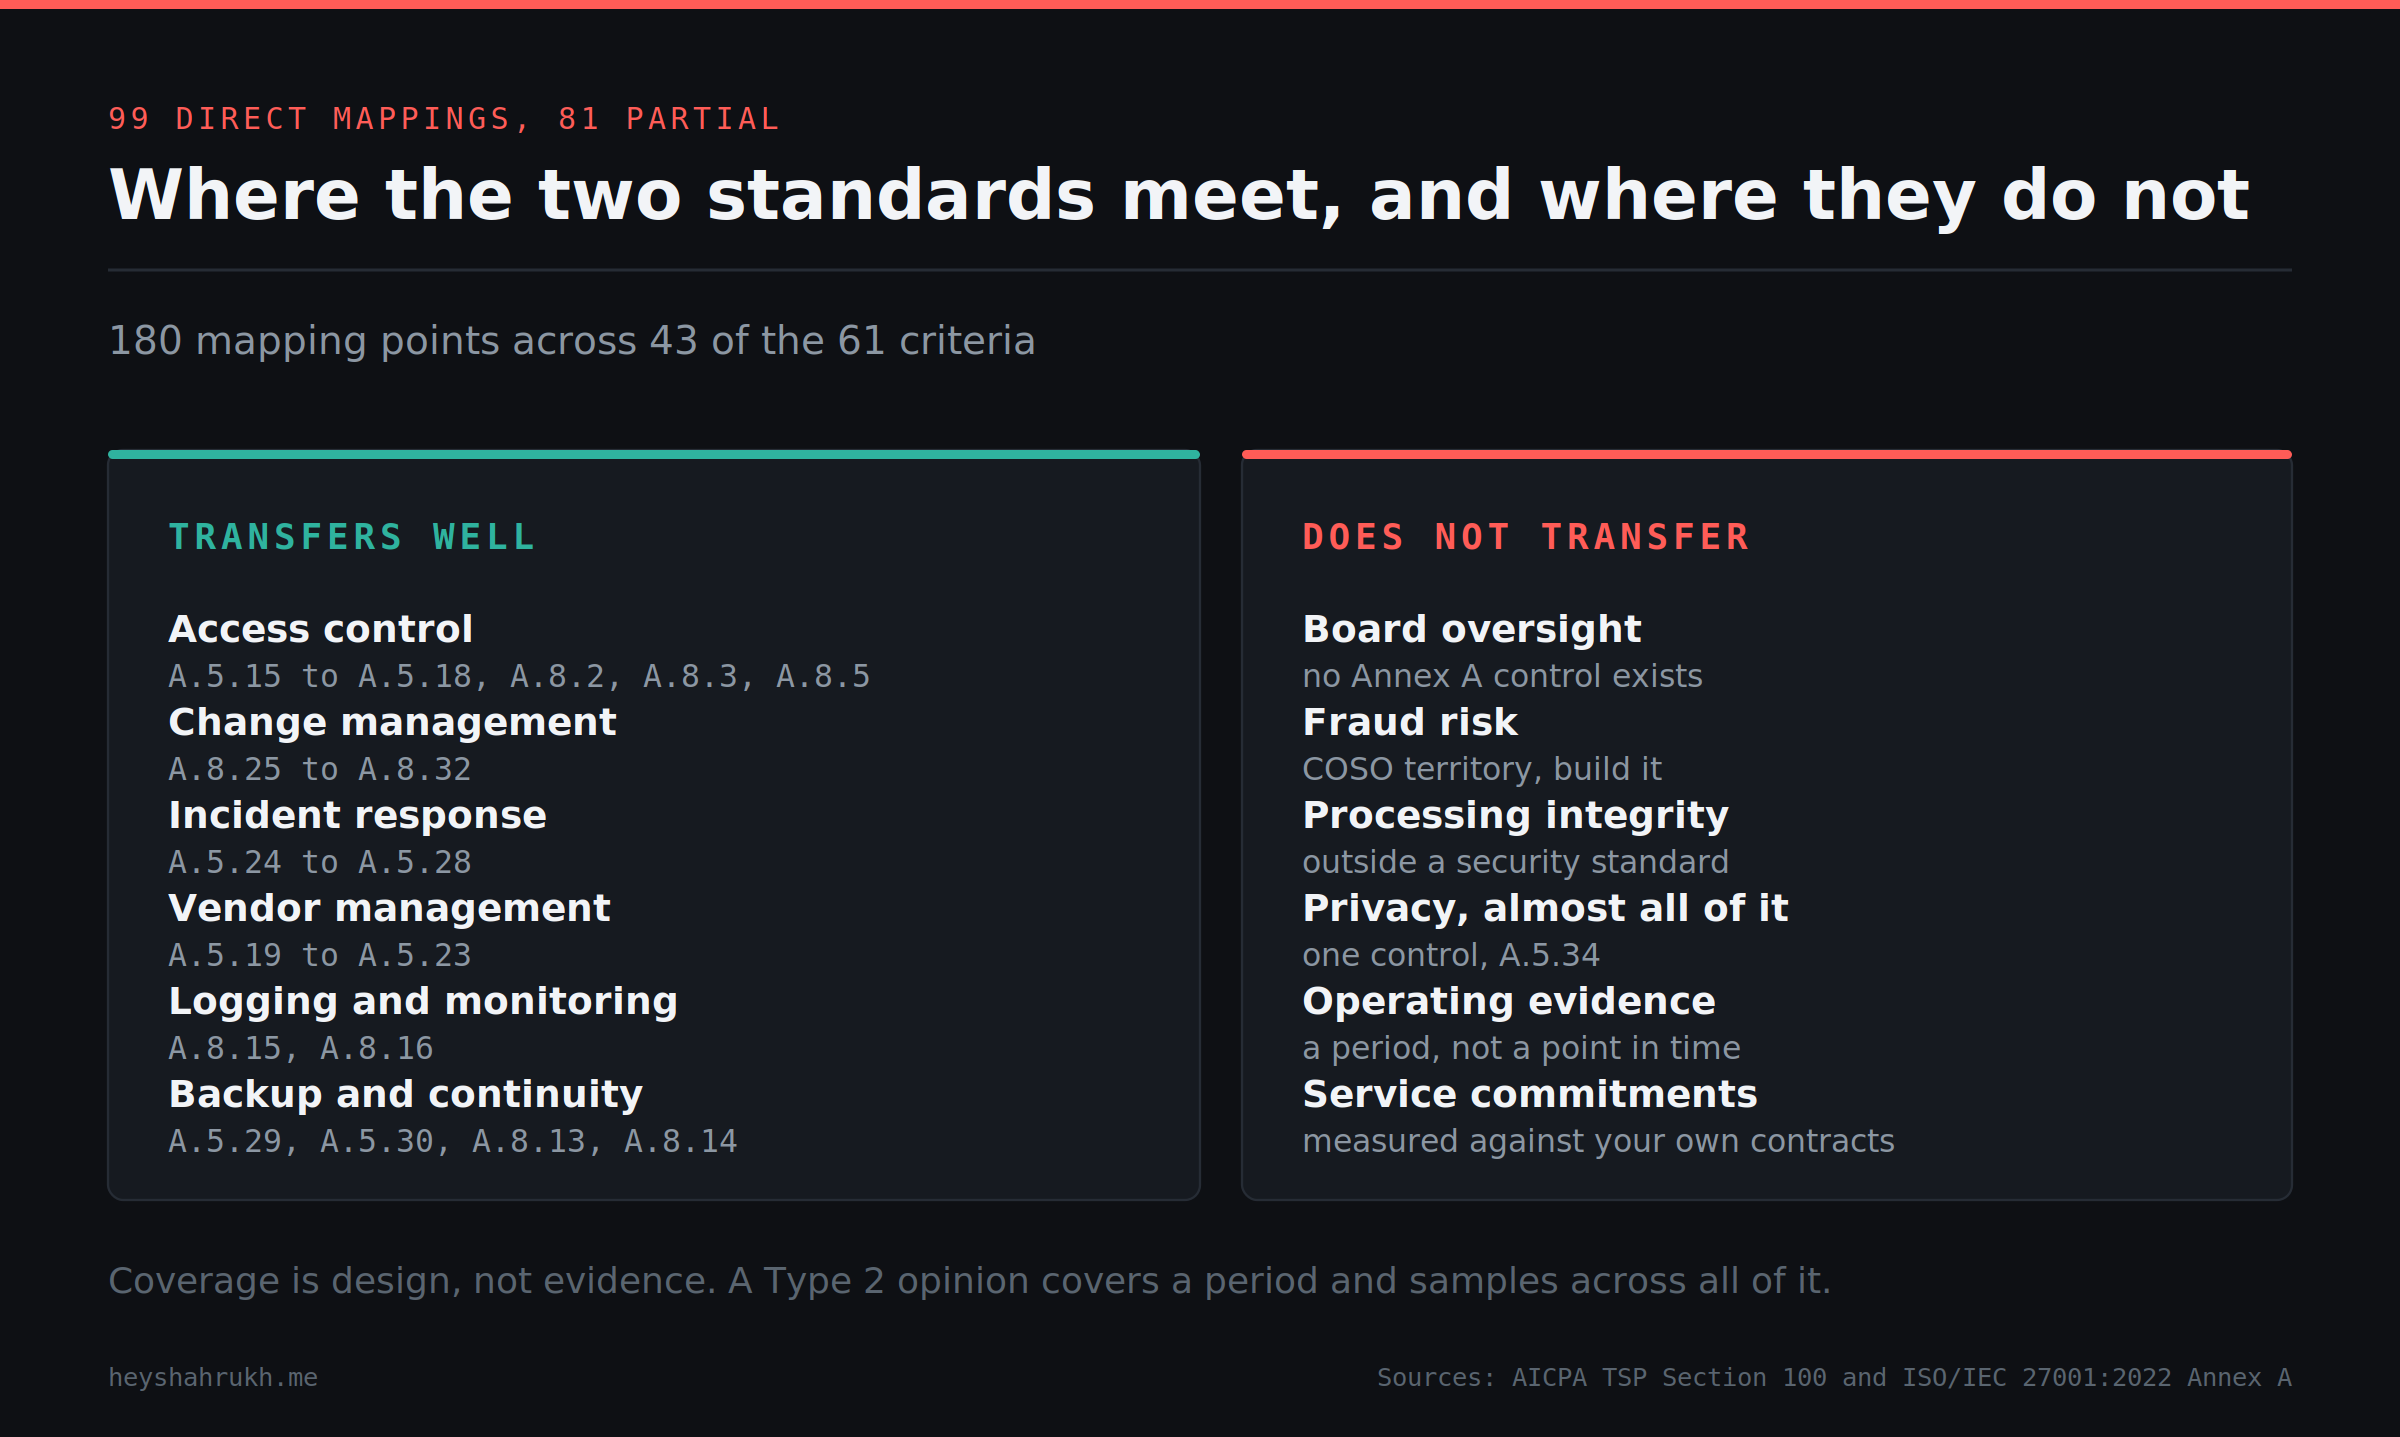
Access control, change management, incident response, vendor management, logging, malware protection, backup and continuity all transfer with little friction. Across the crosswalk there are 180 mapping points touching 43 of the 61 criteria.
Where it does not
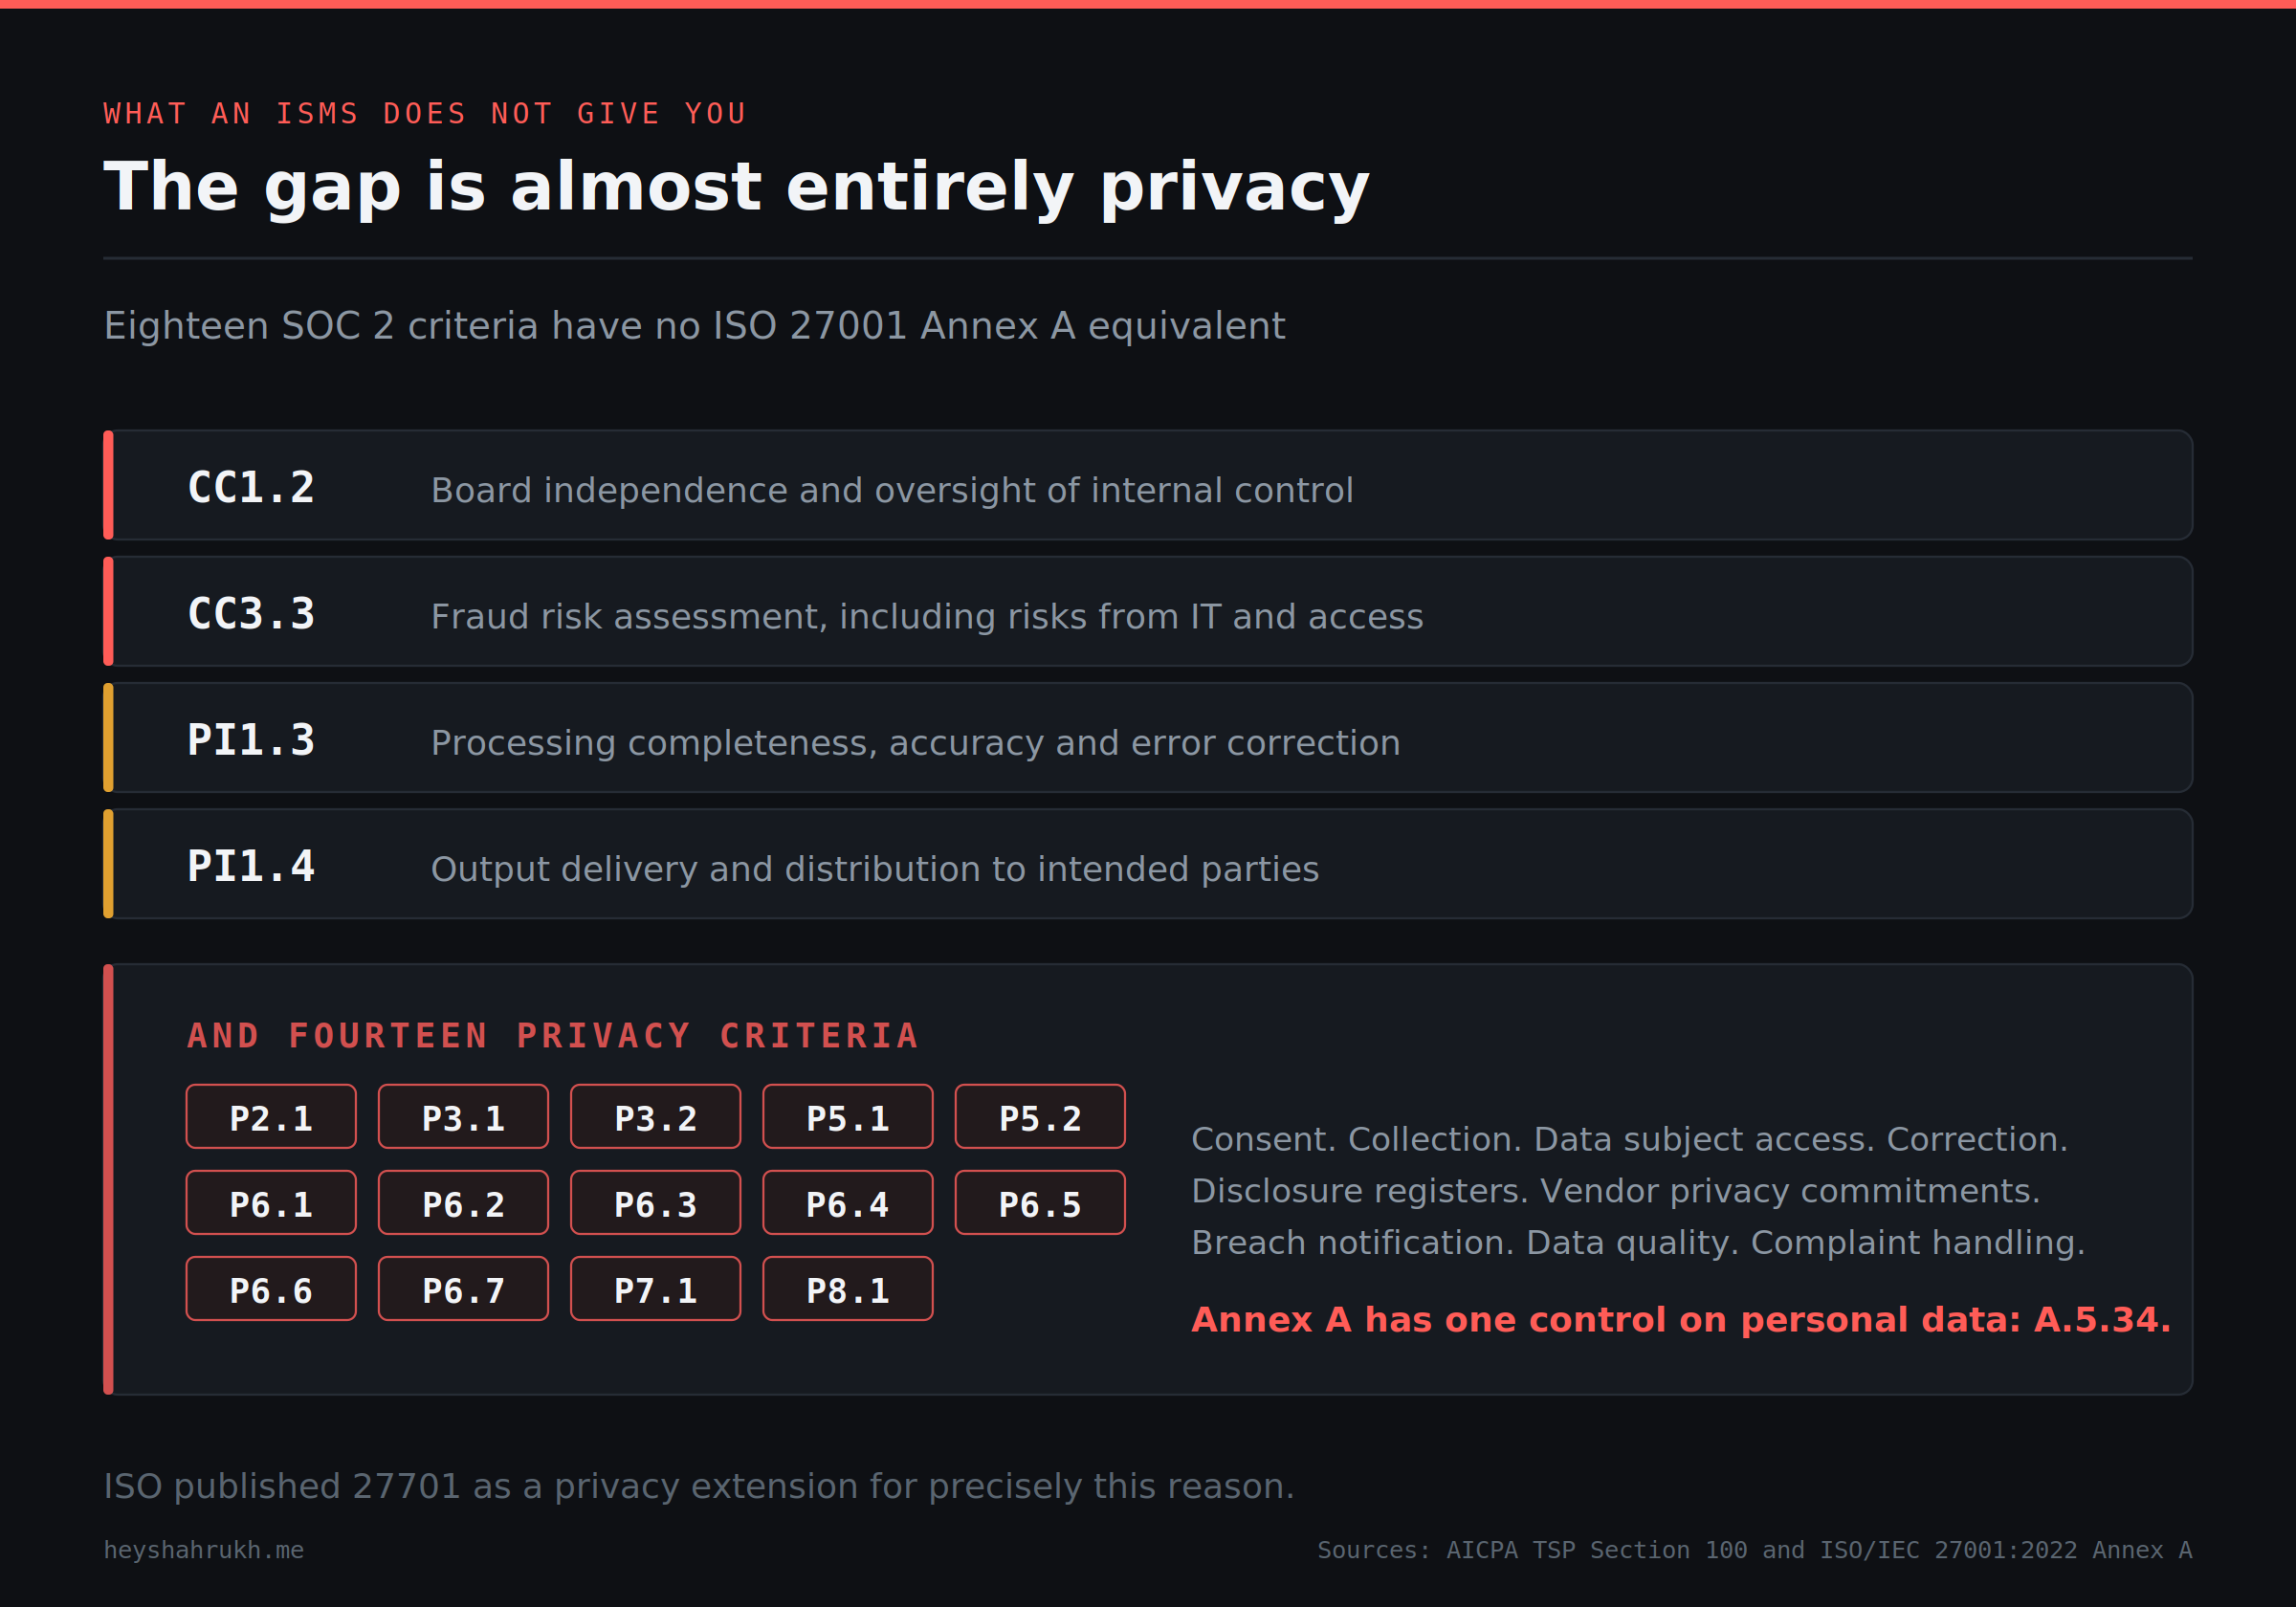
Eighteen criteria have no Annex A equivalent at all. CC1.2, board independence and oversight. CC3.3, fraud risk assessment. PI1.3 and PI1.4, processing and output integrity. And fourteen privacy criteria.
Annex A contains exactly one control about personal data: A.5.34. SOC 2 privacy is eighteen criteria and fifty eight points of focus, plus sixteen more tagged privacy inside the common criteria. Consent mechanics, data subject access, correction rights, disclosure registers, vendor privacy commitments, breach notification, data quality, complaint handling. None of it comes free, and it is not a gap you close in a sprint.
ISO published 27701 as a privacy extension for precisely this reason. If your buyer has not specifically demanded privacy, think hard before selecting it.
Coverage is not evidence
ISO 27001 certification is assessed at a point in time. A SOC 2 Type 2 opinion covers a period, usually twelve months, and the auditor samples across all of it. So seventy percent of your control design transfers. Whether the operating evidence transfers depends entirely on how disciplined your ISMS has been about keeping artefacts with dates on them, and that varies enormously between organisations holding the same certificate.
SOC 2 also measures you against your own promises. The phrase "to meet the entity's objectives" reads as your service commitments and system requirements, so your contracts become audit scope in a way teams rarely expect.
Expect roughly seventy percent to transfer. Expect board oversight, fraud risk and processing integrity to be new. And if privacy is in scope, expect that to be the bulk of the project no matter how good your ISMS is.
Download the tool
ISO 27001 to SOC 2 Coverage Tool is free on the utilities page of this site: heyshahrukh.me/control-room/utils
Set the status of your 93 Annex A controls and the whole workbook recalculates. Crosswalk, criteria coverage, a full register of all 330 points of focus, and a gap analysis sheet. One Excel file, nothing to sign up for.
The mapping is my professional judgement at criterion level, not an AICPA or ISO product. The crosswalk sheet is editable so you can argue your own version with your auditor.
Related posts
- There Is No List of SOC 2 Controls
SOC 2 publishes 61 criteria and 330 points of focus, and exactly zero controls. What the standard actually contains, and how to run readiness against it.
- Email Security Best Practices for Modern Organizations
Explore modern email threats, phishing risks, BEC attacks, and practical security controls to protect your organization from compromise